OpenAudit: one scored audit of everything you ship
What it is
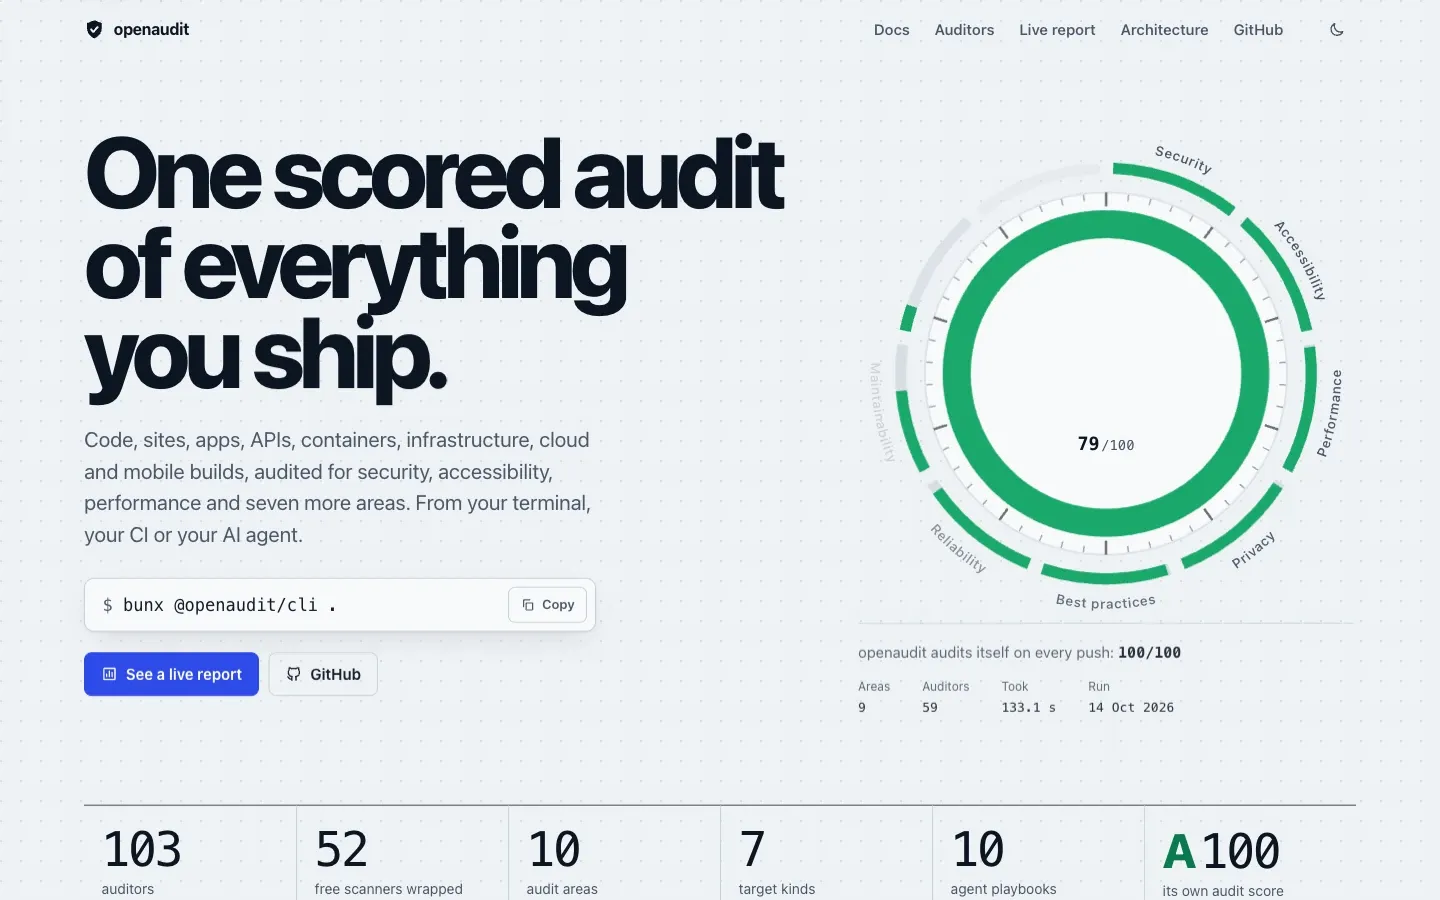
One scored audit of everything you ship: code, sites, apps, APIs, containers, infrastructure, cloud and mobile builds. It runs from the terminal, in CI or from an AI agent over MCP.
Overlapping findings from several tools are merged into one, results come out as HTML, JSON, SARIF, Markdown or CSV, and every target is treated as hostile: nothing in it is built or installed.
How it’s built
Built on Bun with 37 built-in auditors and a set of free scanners wired in, including Semgrep, Trivy, gitleaks, osv-scanner, Lighthouse and axe-core.
There is a GitHub Action, multi-architecture Docker images with an SBOM, and ready-made playbooks for agents that make the judgement calls tools cannot, such as authorisation review and keyboard navigation.
Stack: Bun, TypeScript, MCP, Docker, GitHub Actions, SARIF.
What it shows
The same discipline I bring to client systems: measure, score and fix, with agents as a natural part of the work rather than an afterthought.
- 103
- auditors
- 10
- audit areas
- A 100
- its own score on every push